Find the HIPAA Gaps That Could Cost Your Practice Thousands
Speak directly with Chuck Weiselberg, who has guided practices through OCR audits. No cost, no judgement, no obligation.
- Identify your biggest compliance gaps
- Get actionable next steps you can start today
- Ask any question about HIPAA (federal rules for protecting patient data)
The times shown are in the time zone at the top of the calendar. Check it matches where you are before you pick a time.
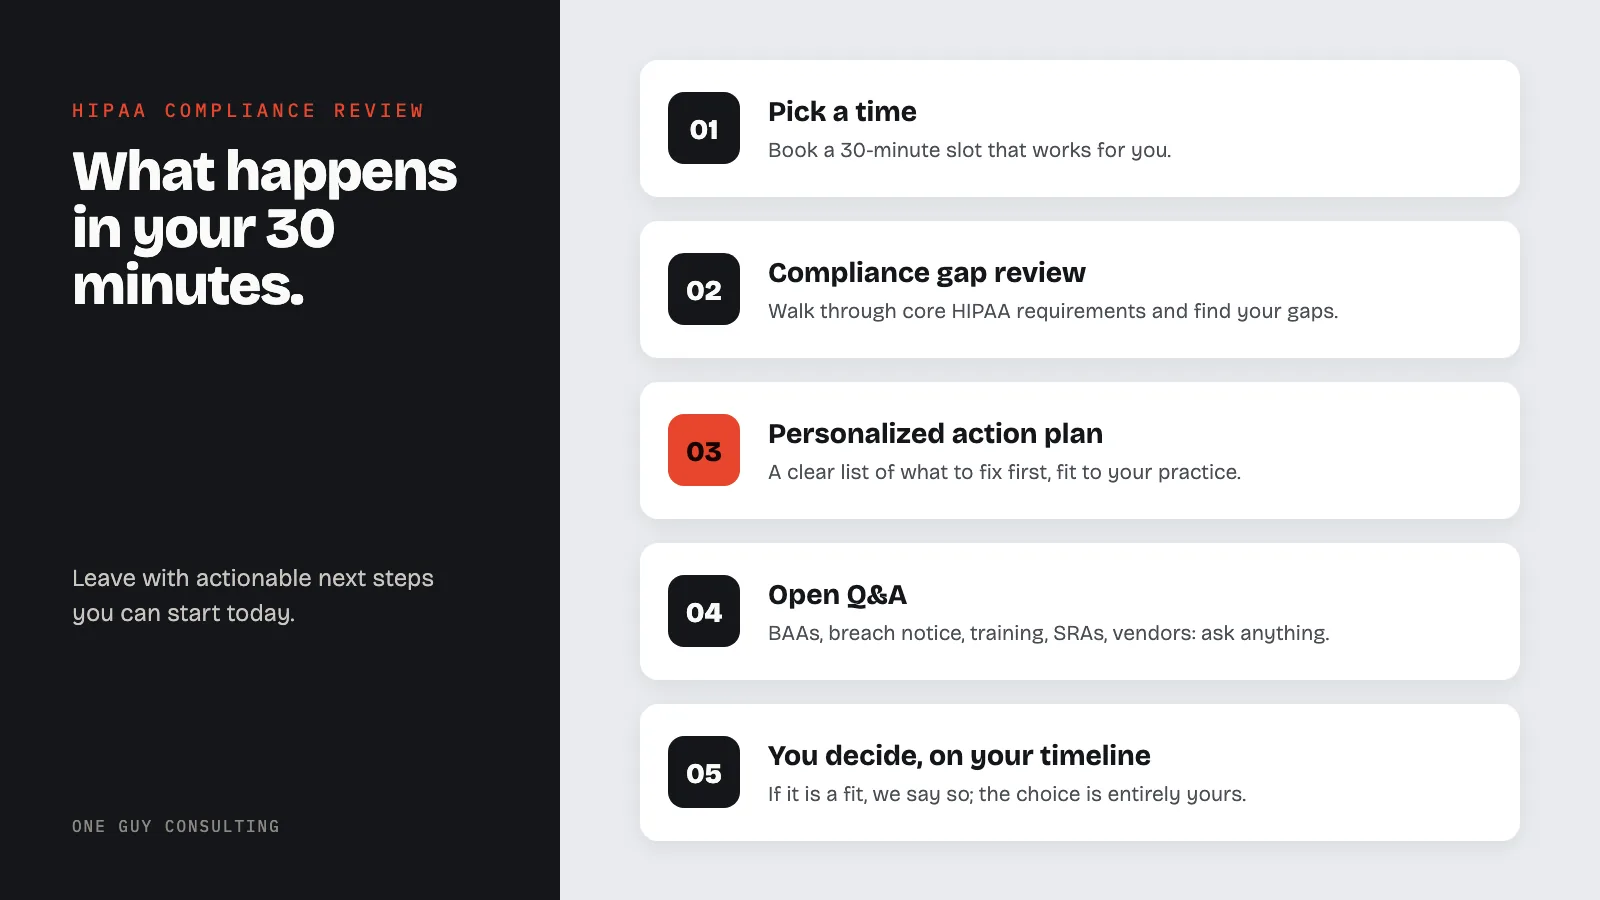
What we cover on the 30-minute call
In 30 minutes, we cover the areas that matter most to your practice.
Compliance Gap Review
We walk through the core HIPAA requirements and identify where your practice has gaps.
Personalized Action Plan
You leave with a clear list of what to fix first. Steps tailored to your practice size and specialty.
Open Q&A
BAAs, breach notification, employee training, security risk assessments, remote work, vendor management. Nothing is off limits.
What Chuck checks with you on the call:
- Whether you have a current Security Risk Assessment, the first thing the HHS Office for Civil Rights asks for (HHS risk analysis guidance).
- Whether your HIPAA policies are written down, and when they were last updated.
- Whether staff training is documented: who was trained, when, and on what.
- Which vendors touch patient data, and whether each one has a signed Business Associate Agreement.
- What you would do if a breach happened tomorrow, including how breaches are reported to HHS (HHS OCR breach portal).
- Any HIPAA question you bring. For background reading, the HHS OCR HIPAA guidance is the official source.
You Talk to the Expert
One Consultant, Start to Finish
No hand-offs between departments. The person on your call is the same person who does the work.
10+ Years, Zero Fines
Over a decade of HIPAA consulting. Not a single client has been fined or failed an OCR audit. See our Case Studies for anonymized client outcomes.
One result from each case study:
- A mental health franchise office in Florida got audit-ready in under a week and passed its state audit. Case 01.
- A solo eye doctor in a rural town finished a full HIPAA program, built around his comfort with technology. Case 02.
- A health group with more than 100 offices lifted take-up of its program by about 17%. Case 03.
- A small multi-specialty practice built a HIPAA workflow its office manager could keep up. Case 04.
- A practice found vendors touching patient data with no BAA, and got every missing BAA signed. Case 05.
- A practice that assumed software was enough moved to a live program with measurable staff take-up. Case 06.
Who should book this call
Small Practices
Solo providers, small clinics, dental offices, therapy practices with 1-50 employees.
Office Managers
The person who got handed "HIPAA compliance" on top of everything else they already do.
IT/MSP Vendors
Technology vendors handling PHI (protected health information, e.g., medical or billing records) who need to prove HIPAA compliance to their healthcare clients.
Multi-Location Orgs
Growing practices that need consistent compliance across multiple sites and teams.
How to prepare for your intro call
Nothing is required. These help the 30 minutes go further:
- Your practice size and number of locations.
- Whether you have written HIPAA policies, and roughly when they were last updated.
- Whether you have ever done a Security Risk Assessment, and when.
- A rough list of vendors that handle patient data: EHR, billing, IT support, email, phones.
- What brought you here: a letter, a vendor or insurance questionnaire, a new hire, or a sense that you are behind.
What happens after your call
You leave with a short list of what to fix first, in order. What you do with it is up to you.
If One Guy Consulting is a fit, Chuck tells you what that looks like and what it costs. There is one plan, Full-Scope: $120 a month, $1,300 for 12 months, or $2,300 for 24 months, flat per location, with no per-user fees and a 90-day money-back guarantee. It includes 4 hours a month of 1:1 implementation calls with Chuck.
If you sign up, you start in the portal by answering the 63 questions of the Security Risk Assessment. The software builds your gap analysis and remediation plan from your answers. See what happens after signup, step by step.
If it is not a fit, you keep the action steps. The decision is yours, on your timeline.
Frequently Asked Questions
Is this really free? What's the catch?+
How long is the intro call?+
Do I need to prepare anything before the call?+
Will I be pressured to buy something?+
Who will I be speaking with?+
I'm not sure if I need HIPAA compliance. Can I still book?+
Ready to Get Started?
Pick a time that works for you. 30 minutes. Free. No strings attached.
The times shown are in the time zone at the top of the calendar. Check it matches where you are before you pick a time.