What Happens After Signup: HIPAA Audit Timeline
Within about six weeks you can be audit-ready: Day 1 kickoff, Week 1 security risk assessment, Weeks 2 to 3 policies, Weeks 3 to 4 staff training, Weeks 4 to 5 BAAs, Week 6 audit review. Your next step is the 30-minute kickoff call.
Your path from today to audit-ready: clear, simple, and fully supported.
Key HIPAA Terms Referenced in This Process
Security Risk Assessment (SRA)
A systematic look at threats and weaknesses that could expose electronic Protected Health Information (ePHI). Required under 45 CFR § 164.308(a)(1), the SRA is the starting point of every HIPAA program. It is also the first thing OCR asks for during an investigation.
Protected Health Information (PHI)
Health information tied to a specific person. This includes medical records, billing data, and insurance details held by a covered entity or business associate. When stored or sent electronically, it is called ePHI.
Business Associate Agreement (BAA)
A required written contract between a covered entity and any vendor that handles PHI. The BAA spells out what the vendor can do with PHI, what safeguards they must use, and how they must report breaches as specified in 45 CFR § 164.502(e).
Privacy Officer
The person your organization picks to own HIPAA privacy policies. Required under 45 CFR § 164.530(a)(1), the Privacy Officer is your main compliance contact. They are the first user set up in the One Guy Consulting portal.
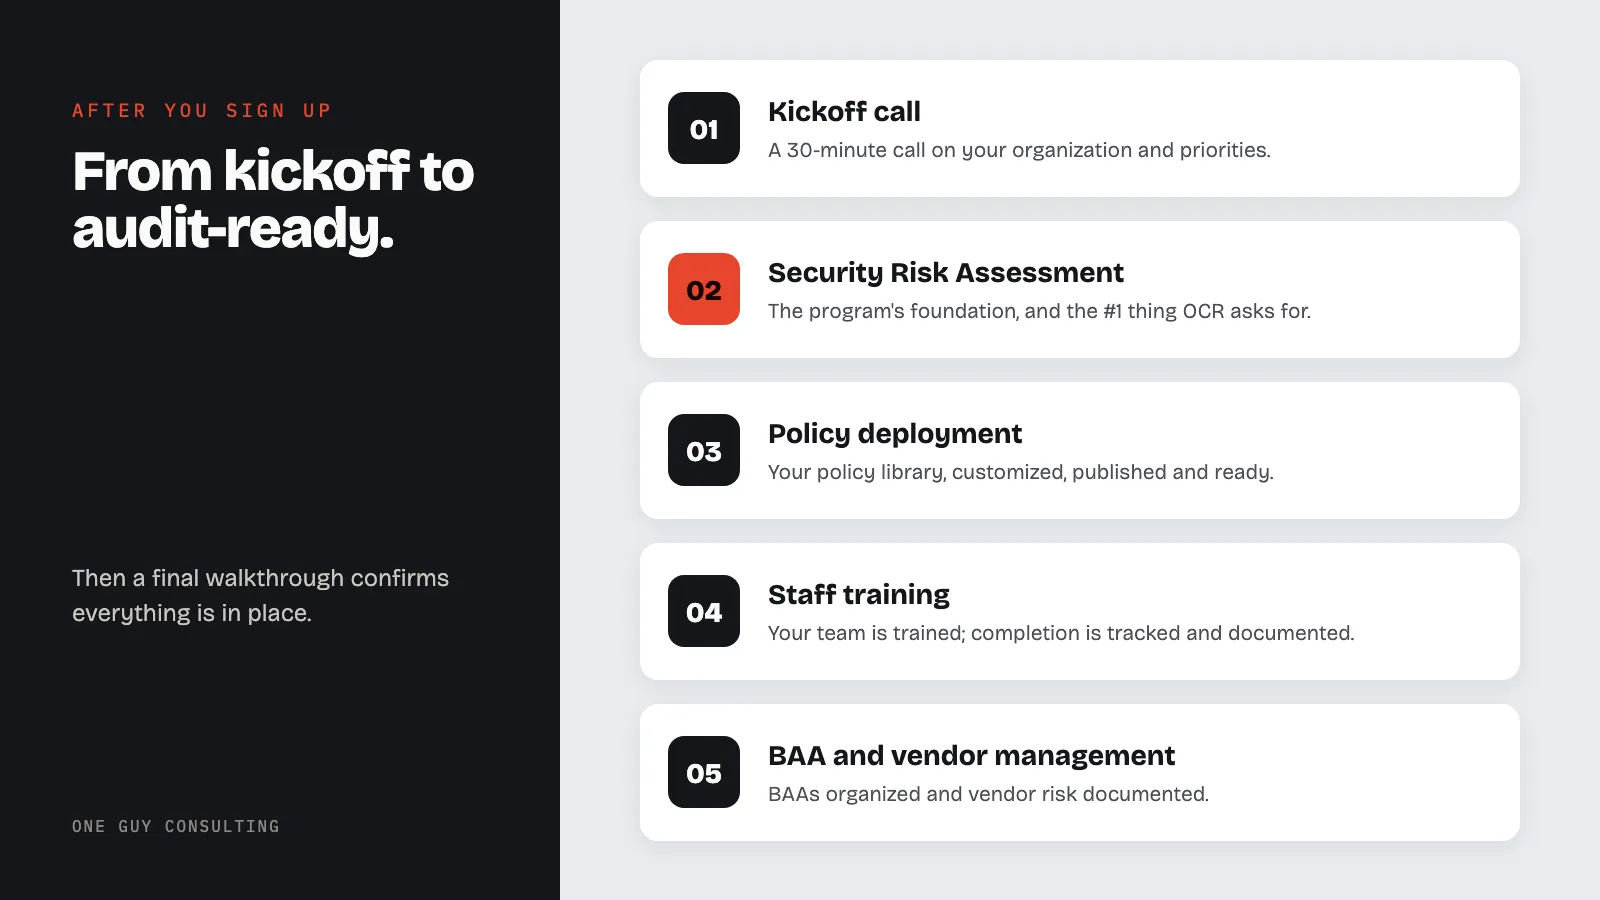
From kickoff to audit-ready
Kickoff Call (Day 1)
A focused 30-minute call to understand your organization, your current state, and your priorities.
- Identify your organization type (Covered Entity or Business Associate)
- Understand your current compliance posture
- Set timeline expectations and assign your Privacy Officer portal access
Security Risk Assessment (Week 1)
The foundation of your entire compliance program, and the #1 thing OCR asks for.
- Guided risk assessment through your portal, no spreadsheets or guesswork
- Identify threats, vulnerabilities, and current safeguards
- Generate your documented risk analysis (required by 45 CFR § 164.308; see HHS's Guidance on Risk Analysis)
What the regulation actually says:
“Risk analysis (Required). Conduct an accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information held by the covered entity or business associate.”
Policy Deployment (Weeks 2 to 3)
Your full HIPAA policy library: customized, published, and ready for your workforce.
- Policies tailored to your organization's size, type, and operations
- Covers Privacy Rule, Security Rule, and Breach Notification
- Published to your branded compliance portal, accessible anytime
Deliverables and audit artifacts:
- A written policy library with an effective date on every policy (45 CFR § 164.316(b)(1))
- Staff acknowledgment records showing who read and accepted each policy
- Version history, kept for six years from creation or last effective date (164.316(b)(2)(i))
Staff Training (Weeks 3 to 4)
Your team gets trained, with completion tracked and documented for audit evidence.
- Role-based training modules assigned to each employee
- Completion tracking with attestation records
- Annual refresher reminders built in
Deliverables and audit artifacts:
- A training log: each workforce member, the module, the completion date and the knowledge-check result (45 CFR § 164.530(b), 164.308(a)(5))
- Policy attestation records tied to each person
- A record of new hires trained within a reasonable period after joining
BAA & Vendor Management (Weeks 4 to 5)
Get your Business Associate Agreements organized and your vendor risk documented.
- BAA generation and tracking through your portal (see HHS's Business Associates guidance)
- Vendor inventory with risk categorization
- Due diligence documentation for each vendor relationship
Audit Readiness Review (Week 6)
A final walkthrough to confirm everything is in place: policies, training, risk assessment, BAAs.
- Compliance gap check against all HIPAA requirements
- Remediation plan for any remaining items
- Your organization is audit-ready
Continuous Compliance
Compliance isn't a one-time project. Your portal keeps you current, year after year.
- Annual risk assessment reminders and updates
- Training renewal tracking
- Incident management and breach notification tools
- Policy updates as regulations change
Typical timeline for small-to-mid-size organizations. Your timeline may vary based on organization size and complexity.
The timeline at a glance
| When | Phase | What you have at the end |
|---|---|---|
| Day 1 | Kickoff call | Organization type identified, timeline set, Privacy Officer portal access assigned |
| Week 1 | Security Risk Assessment | Documented risk analysis (45 CFR § 164.308) |
| Weeks 2 to 3 | Policy deployment | Written policy library with effective dates, staff acknowledgment records, version history |
| Weeks 3 to 4 | Staff training | Training log with completion dates, policy attestation records |
| Weeks 4 to 5 | BAA and vendor management | BAA tracking, vendor inventory with risk categorization, due diligence documentation |
| Week 6 | Audit readiness review | Compliance gap check and a remediation plan for any remaining items |
| Ongoing | Continuous compliance | Annual risk assessment reminders, training renewal tracking, incident management, policy updates |
What happens after signup: FAQ
How long until we are audit-ready?
Typical six-week timeline: Day 1 kickoff; Week 1 SRA; Weeks 2 to 3 policy deployment; Weeks 3 to 4 staff training; Weeks 4 to 5 BAAs; Week 6 audit review.
What happens on the kickoff call?
A focused 30-minute call to identify your organization type, assess current posture, set timeline expectations, and assign your Privacy Officer portal access.
Who is the first portal user?
The Privacy Officer is the first user set up in the One Guy Consulting portal.
How is the Security Risk Assessment delivered?
A guided risk assessment through your portal that generates the documented risk analysis required by 45 CFR § 164.308.
What ongoing support does the portal provide?
Annual risk assessment reminders, training renewal tracking, incident management, and policy updates via the portal.
See the Case Studies page for client remediation examples and outcomes that show audit-readiness in practice. One example: a mental health franchise office in Florida with no program in place got audit-ready in under a week, passed its state audit, and kept seeing patients (case 01).
What We Promise
No Wasted Time
Guided process: we tell you exactly what's needed at each step
Full Picture
Privacy, Security, and Breach Notification Rules, all addressed in one program
Built for Humans
Policies written so your staff can actually read, understand, and follow them
One Guy Consulting in 37 seconds
Ready to get started?
Let's book your kickoff. Want more detail on each phase? Read the complete HIPAA compliance process.