HIPAA compliance consulting for dental practices.
Dental practices are covered entities under HIPAA when they send health data in digital form as part of a covered transaction, such as filing claims with a health plan (45 CFR 160.103). That includes solo offices, group practices, dental service organizations (DSOs), and specialties like orthodontics, periodontics, and oral surgery. For a full overview of what dental offices need to address, see our guide to HIPAA compliance for dental practices.
Yes.Whenever the practice transmits health information electronically.
There is no size exemption. A solo dentist who files claims online faces the same rules as a large DSO.
The risks that are specific to dentistry.
PHI (protected health information: individually identifiable health information about a patient's condition, treatment, or payment) in a dental office includes intake forms, treatment plans, clinical notes, imaging files, insurance claims, appointment records, and billing data. Any data that names a patient and relates to their dental care, payment, or health plan counts as PHI under 45 CFR 160.103. These are the places it most often slips.
Digital X-rays, CBCT, and intraoral images
Imaging data is ePHI (PHI created, received, maintained, or transmitted in electronic form). It needs access controls, audit logs, and secure sending, and the imaging vendor must sign a BAA before any PHI is stored in or sent through their system.
Shared imaging workstations
Imaging workstations must enforce unique user authentication, and imaging vendors must not store or transmit patient data outside the scope of their signed BAA.
Texted and emailed reminders
Reminders are allowed for treatment, but contact choices belong in your NPP and requests for limits must be honored. A reminder that names the procedure carries more PHI risk than one with just the date and time.
Paper charts, printers, and shared screens
Physical safeguards cover paper charts and printed treatment plans. Gap reviews commonly surface printer placement, shared workstation access, and paper storage issues that are simple to fix once found.
IT, cloud, billing, and imaging vendors with no BAA
Many dental offices have no BAAs (Business Associate Agreements: the written contract, required under 164.502(e), that sets what a vendor may do with PHI) with IT or imaging vendors. The BAA should cover the data types the vendor handles, including old image files and any cloud backup the vendor runs.
Multi-location groups
DSOs face added work setting up uniform policies across offices with different EHR systems, staffing, and state rules. An organization-level gap analysis is the right starting point before aligning policies across sites.
What fixing these gaps looks like.
Three anonymized results from my case studies. None of them is a dental office. I include them because the same gaps (missing BAAs, unwritten policies, unfinished training) are on the dental risk list above.
Every missing BAA signed
Before: a single-location practice had several vendors handling PHI with no BAA. After: every missing BAA was signed, and the practice now runs a repeatable vendor review.
Audit-ready in under a week
Before: a Florida mental health franchise office had policies that were never written, records with holes, and training half done, with a state auditor due in days. After: it was audit-ready in under a week and passed its state audit.
A solo office, start to finish
A rural solo optometrist finished a full HIPAA program. Solo dental offices face the same rules, with no size exemption.
Three rules. Here is what each one means in a dental office.
How PHI is used and shared
- Give patients a Notice of Privacy Practices (NPP)
- Honor patient rights to view and fix records
- Share only the least PHI needed for the task
Safeguards for electronic PHI
- Administrative, physical, and technical safeguards
- Practice management software and email
- X-rays, CBCT, intraoral cameras, and cloud backups
What to do when PHI leaks
- A breach of unsecured PHI is the acquisition, access, use, or disclosure of PHI in a way the Privacy Rule does not permit that compromises its security or privacy (164.402)
- Notify affected patients within 60 days of discovery (164.404)
- 500 or more affected: also report to HHS (164.408) and prominent media (164.406)
- A documented incident management process covering breach detection, risk assessment, and notice timelines keeps you inside the 60-day window
without unreasonable delay and in no case later than 60 calendar days after discovery of a breach.45 CFR 164.404(b)
Implement procedures to verify that a person or entity seeking access to electronic protected health information is the one claimed.45 CFR 164.312(d)
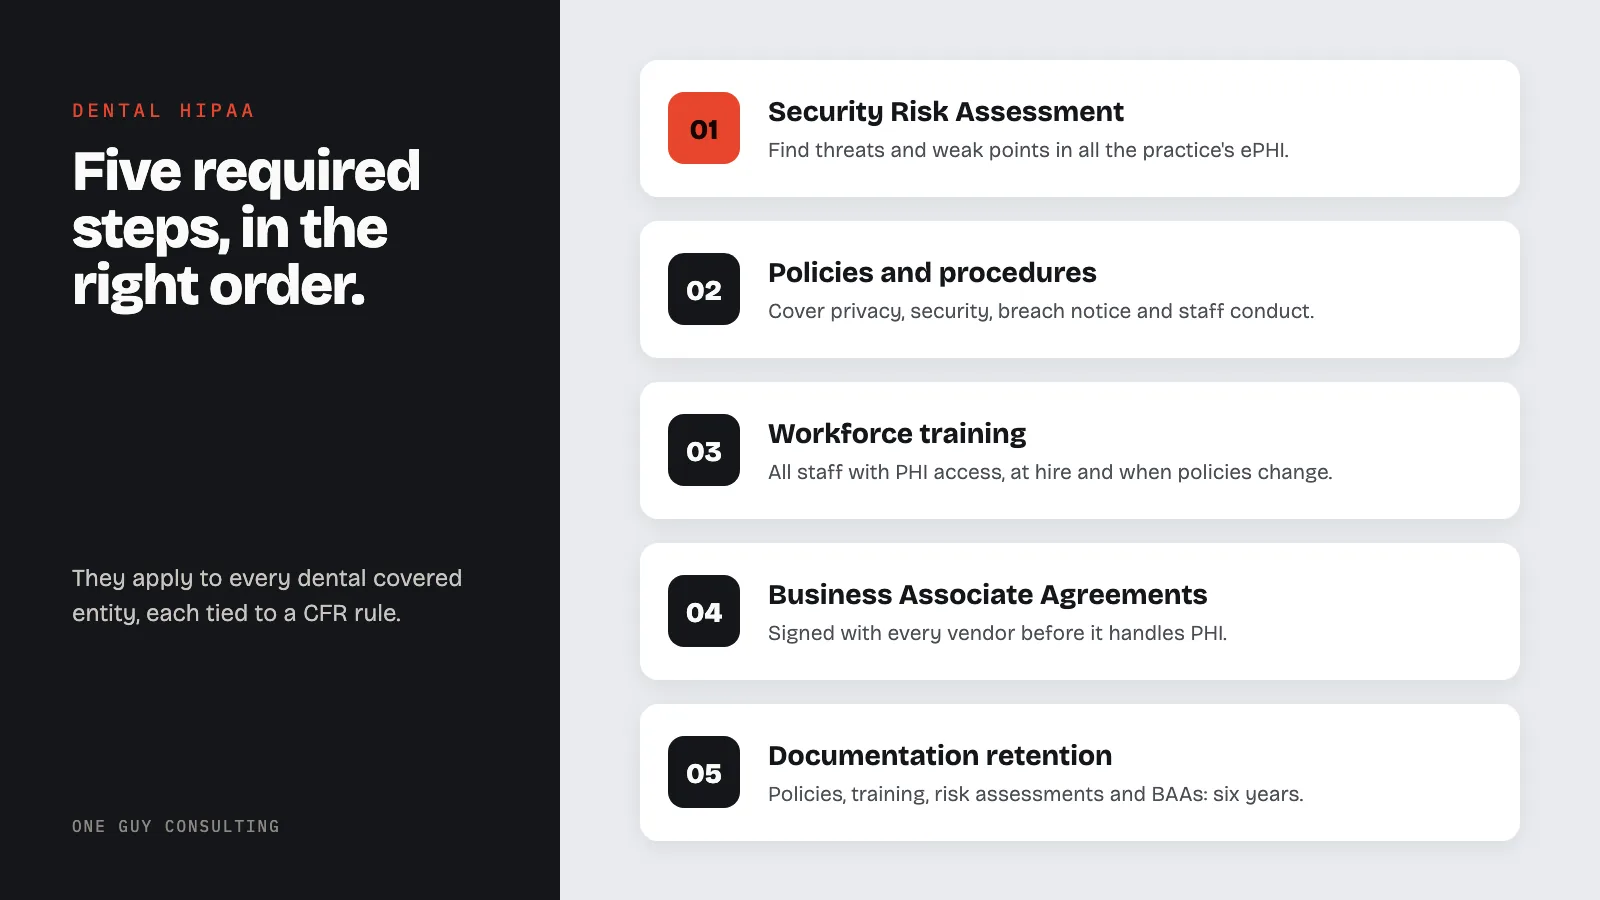
Five required steps, done in the right order.
These steps apply to every dental covered entity. Each ties to a specific CFR rule and carries its own fine risk if left undone. See our HIPAA compliance cost breakdown for what practices typically spend.
- 01
Security Risk Assessment
Find threats and weak points in all ePHI the practice creates, receives, stores, or sends. A documented risk assessment is the most common missing item when OCR looks into dental practices.
Start hereAlmost everything else builds on it. - 02
Written policies and procedures
Cover privacy, security, breach notice, and staff conduct. Dental-specific policy templates skip vague language and match real workflows like imaging room access, patient check-in, and insurance billing.
Dental fitImaging rooms, check-in, and insurance billing. - 03
Workforce training
All staff with PHI access (front desk, hygienists, assistants, and billing staff) get HIPAA training at hire and when policies change. Yearly refreshers are best practice.
Keep the proofDate, topics, and each person's name, for six years. - 04
Business Associate Agreements
Required before any vendor handles PHI. Signed with IT providers, cloud storage vendors, billing services, imaging software companies, and any other entity that handles PHI for the practice. We track them with BAA management.
Check the scopeOld image files and vendor-run cloud backups included. - 05
Documentation retention
Policies, training records, risk assessments, and BAAs are kept for six years, organized so you can hand them over when OCR asks.
First requestOCR often asks for training records first.
| Step | What it means in a dental office | Rule |
|---|---|---|
| Security Risk Assessment | Find threats to all ePHI: practice management software, X-rays, CBCT, email, and cloud backups. | 164.308(a)(1)(ii)(A) |
| Policies and procedures | Written policies that match imaging room access, patient check-in, and insurance billing. | 164.316(a) |
| Workforce training | Front desk, hygienists, assistants, and billing staff trained at hire and when policies change. | 164.308(a)(5)(i) |
| Business Associate Agreements | Signed before IT, cloud, billing, or imaging vendors handle PHI, including old image files and backups. | 164.502(e) |
| Documentation retention | Policies, training records, SRAs, and BAAs kept for six years. | 164.530(j) |
Not sure where you stand? A gap analysis ties each gap to the CFR rule it breaks and ranks fixes by fine risk.
Where dental practices usually fall short.
A structured gap analysis ties each gap to the CFR rule it breaks and ranks fixes by fine risk. For multi-location DSOs, a gap analysis at the organization level is the right starting point before aligning policies across sites.
OCR looks into dental practices too.
The Office for Civil Rights (OCR) enforces HIPAA for all covered entities, including dental practices. Fines range from $145 to $2,190,294 per violation type per year under 45 CFR 160.404.
OCR has looked into dental practices for:
- Complaints about unauthorized sharing
- Missing risk assessments
- Failure to give patients their records within 30 days, per 164.524(b)(2)
Official guidance from HHS: HIPAA for professionals, the Security Rule, risk analysis guidance, and the Breach Notification Rule.
There is no size exemption. A solo office and a large DSO face the same requirements.
One flat price for the whole dental office.
One plan, three ways to pay. No per-user fees, so adding a hygienist or a front-desk hire does not change your bill. Every step above is covered.
- The full platform: SRA, gap analysis, remediation plans
- Policy templates and staff training
- Vendor and BAA management
- 4 hours a month of 1:1 implementation calls with Chuck
- Incident response guidance
- CMS audit response support
One payment, two full years of coverage.
Flat rate per location.
Secure checkout by Stripe. Your payment details go straight to Stripe and never touch our servers.
Dental HIPAA, answered.
Are dental practices required to comply with HIPAA?+
Do dental imaging systems have specific HIPAA requirements?+
How often must dental staff complete HIPAA training?+
Does HIPAA apply to paper records in dental offices?+
Can dental practices text appointment reminders to patients?+
One Guy Consulting in 37 seconds
Find the gaps in your practice before OCR does.
One Guy Consulting is based in Queens, New York, and works with dental offices nationwide: solo offices, group practices, and multi-location DSOs.