Direct answer: Sprinto is a compliance automation platform (software that collects audit evidence and monitors controls) for SOC 2, ISO 27001, and other audit frameworks. It is not a dedicated HIPAA compliance solution. It can help organize HIPAA-related evidence, and its pricing page lists periodic risk assessments, AI-assisted policies, ready-to-use training, and periodic vendor reviews (checked November 7, 2026). Your team still conducts the HIPAA risk analysis under 45 CFR 164.308(a)(1), adapts the policies, runs workforce training, and puts BAAs (Business Associate Agreements, the contracts HIPAA requires with vendors that handle patient data) in place under 45 CFR 164.502(e).
Organizations whose primary or only compliance need is HIPAA will find gaps between what Sprinto automates and what HIPAA requires.
Thinking about Sprinto? You are likely looking for a way to automate compliance and make audit prep easier.
Sprinto is built to help companies manage frameworks like SOC 2 and ISO through integrations and continuous monitoring. But for HIPAA, there is one key thing to know:
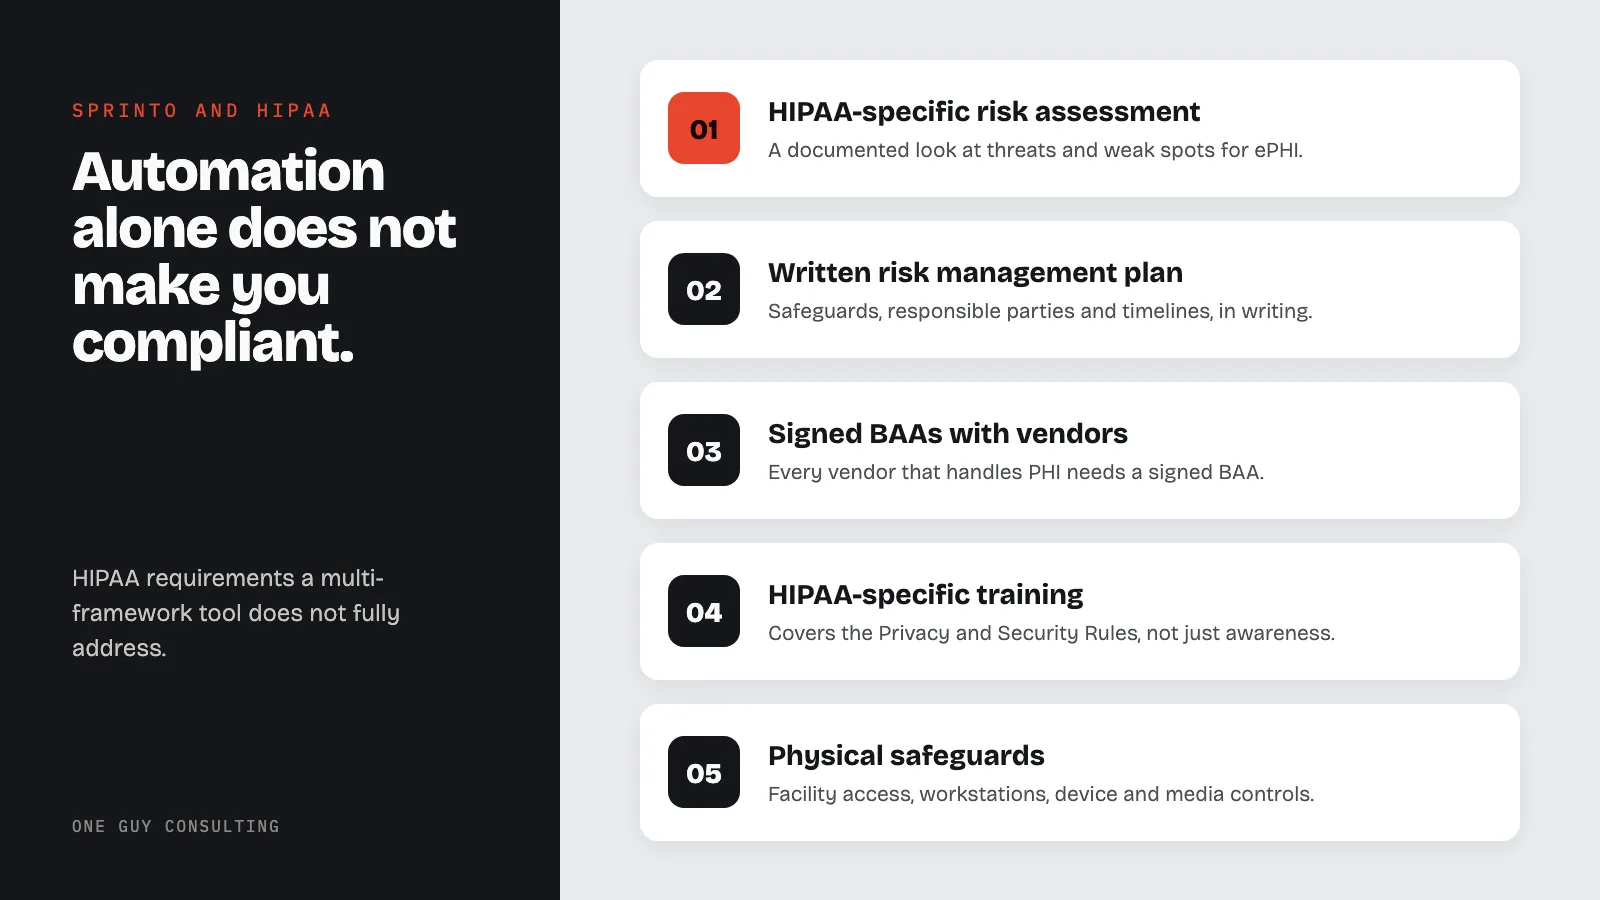
Automation helps you stay organized. It does not get you compliant on its own.
This article compares Sprinto and One Guy Consulting. I run One Guy Consulting, so read it knowing I sell the other option. The Sprinto details below come from Sprinto's own pricing and HIPAA pages, which I checked on November 7, 2026.
Sprinto vs One Guy Consulting at a Glance
| Feature | Sprinto | One Guy Consulting |
|---|---|---|
| Primary frameworks | 25+ frameworks automated, including SOC 2, ISO 27001, GDPR, PCI DSS and HIPAA | HIPAA (primary and only focus) |
| HIPAA-specific risk assessment | Periodic risk assessments, a risk library, and risk treatment plan tracking | HIPAA Security Risk Assessment under 45 CFR 164.308(a)(1)(ii)(A) |
| Policy templates | AI-assisted policies and out-of-the-box HIPAA policy templates | HIPAA-specific policy templates mapped to 45 CFR 164.316 |
| Workforce training | Ready-to-use training and tests | HIPAA-specific training under 45 CFR 164.308(a)(5) |
| BAA management | Vendor risk management with periodic vendor reviews | BAA tracking and execution under 45 CFR 164.502(e) |
| Support model | 24x5 priority email and in-app support; a dedicated CSM on the Growth plan | Full-Scope: 4 hours a month of 1:1 implementation calls with Chuck. |
| Technical requirement | Built on integrations: monitoring across 300+ of them | Minimal: guided workflow, no integrations needed |
| Approach | Evidence collection and monitoring automation | Execution-first: gap analysis, remediation, completion |
| Best for | Tech companies managing multiple audit frameworks | Healthcare teams and BAs whose primary need is HIPAA |
Sprinto column sources: Sprinto pricing and Sprinto HIPAA page.
What Sprinto Does Well
Sprinto's pricing page lists a Foundation plan, For startups on their first certification
, and a Growth plan, For teams automating compliance
.
Strengths include:
- Automated evidence collection via integrations
- Continuous monitoring of systems and controls
- Simpler audit prep workflows
- A public trust center with a custom domain
If your team has technical staff, needs to manage multiple frameworks, and wants automation on top of existing systems, it is a solid pick.
Where Sprinto May Not Fit HIPAA-Focused Companies
Sprinto is strong at automation. But it is built for audit-based frameworks, not the day-to-day realities of HIPAA compliance.
Built for Audit Frameworks, Not HIPAA-First
Sprinto works best for frameworks like SOC 2. In those, compliance is shown through collected evidence. HIPAA is different. It requires a documented security risk analysis under 45 CFR 164.308(a)(1)(ii)(A), implementation of administrative, physical, and technical safeguards under 45 CFR 164.308-312, and ongoing risk management under 45 CFR 164.308(a)(1)(ii)(B). That creates a gap between tracking compliance and actually achieving it. A gap-first approach to risk assessment covers the practical side that audit tools often miss.
Automation Supports. It Doesn't Execute.
Sprinto helps you organize compliance, collect evidence, and monitor controls. But you still need to conduct a thorough risk analysis, implement required safeguards across all three categories (administrative, physical, and technical per 45 CFR 164.308-312), execute workforce training under 45 CFR 164.308(a)(5), and document every step. Automation assists the process. The work itself is still yours.
Requires Ongoing System Work
To get full value from Sprinto, you connect your systems (Sprinto names AWS, GCP, Azure, Okta, Google Workspace and GitHub), keep them connected, and act on what the monitors flag. For healthcare teams, this can add complexity instead of cutting it.
Specific HIPAA Gaps in Sprinto
The risk analysis is where HIPAA starts. Here is the requirement, word for word:
"Risk analysis (Required). Conduct an accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information held by the covered entity or business associate."
45 CFR 164.308(a)(1)(ii)(A)
These are the HIPAA requirements where a multi-framework tool still leaves the work with your team:
- Security Risk Assessment (45 CFR 164.308(a)(1)(ii)(A)). HIPAA requires a documented risk assessment that identifies threats and vulnerabilities specific to ePHI (electronic protected health information). OCR enforces it through its Risk Analysis Initiative; an August 18, 2025 settlement was the initiative's 10th enforcement action. Whatever tool you use, the analysis has to be scoped to ePHI and documented.
- Risk management plan (45 CFR 164.308(a)(1)(ii)(B)). After the risk assessment, HIPAA's risk management standard says:
Implement security measures sufficient to reduce risks and vulnerabilities to a reasonable and appropriate level
. Sprinto's pricing page lists risk treatment plan record and tracking, so the plan has a place to live. Choosing the safeguards, owners and dates is still your team's work. - Business Associate Agreement management (45 CFR 164.502(e)). Every vendor that creates, receives, maintains, or transmits PHI needs a signed BAA. Reviewing a vendor is not the same as having its signed agreement on file. A single-location practice I worked with found several vendors touching PHI with no BAA in place; it got every missing BAA signed and set up a vendor review it can run again (Case 05).
- HIPAA-specific workforce training (45 CFR 164.308(a)(5)). HIPAA training must cover topics specific to the HIPAA Privacy and Security Rules - not just general security awareness. The content and the training records you keep differ from SOC 2 training.
- Physical safeguards (45 CFR 164.310). HIPAA requires facility access controls, workstation security, and device and media controls. Sprinto's HIPAA page says its compliance team helps align physical safeguards and that it validates devices. The facility side (door locks, visitor logs, who can enter where) still happens in your building and gets documented by your team.
- Breach notification procedures (45 CFR 164.400-414). HIPAA has specific breach notification timelines and requirements (60 days to individuals; HHS is notified at the same time as individuals for breaches affecting 500+). These differ from incident response procedures in SOC 2 or ISO frameworks.
Where One Guy Consulting Is Different
One Guy Consulting was built with a different goal:
Help companies become fully HIPAA compliant without managing complex systems.
Execution vs. Automation
Instead of integrations and monitoring, One Guy Consulting provides:
- Automated gap analysis to find compliance gaps
- Automated fix plans to resolve them
- A centralized, cloud-based system for full-scope compliance
No complex setup. No technical overhead. No guesswork.
Built Specifically for HIPAA
One Guy Consulting was designed for HIPAA compliance from the start. On Full-Scope calls, I walk you through the software and the process step by step until the work is done. I do not interpret the law for you; for that, talk to a lawyer.
The right pick depends on what you need. Do you need a multi-framework audit tool? Or a focused HIPAA solution?
The Stakes Are Higher Than They Used to Be
Whatever you choose, doing nothing is not an option. The HHS Office for Civil Rights (OCR) enforces HIPAA through investigations and civil monetary penalties under 42 USC 1320d-5. HIPAA fines went up again in 2026. OCR has shown it will go after small practices and business associates, not just big health systems.
A 2025 enforcement breakdown counted 21 actions in one year. That is the second-highest annual total ever. The common threads in cases like these are a risk analysis that was never completed, required safeguards that were never put in place, and missing BAAs with vendors handling PHI.
The question is not whether you need HIPAA compliance. It is whether an audit tool is the right fit, or whether you need a solution built for HIPAA execution.
Who Should Use Each?
Choose Sprinto if:
- You manage SOC 2 or ISO frameworks
- You have technical staff to manage integrations
- You want automated audit prep across multiple standards
Choose One Guy Consulting if:
- You need to become HIPAA compliant
- You do not want to manage integrations or systems
- You want a direct, execution-focused solution
- You prefer simplicity and speed over multi-framework coverage
Final Take
Sprinto is a strong automation tool for managing compliance frameworks. It is a great fit for startups and tech companies managing SOC 2 or ISO alongside HIPAA.
But HIPAA needs execution, not just organization.
One Guy Consulting is built for teams that want to get compliant without managing a tool designed for a different purpose. If you are a business associate trying to understand your duties before picking a solution, start with the common BAA mistakes that lead to fines. It gives a clear picture of what full compliance actually takes.
Ready to get HIPAA compliant without dealing with integrations, dashboards, and ongoing system work? One Guy Consulting is built for small healthcare teams and business associates that want to get compliant fast, with someone walking them through it. Get started with One Guy Consulting
One Guy Consulting in 37 Seconds
Key HIPAA Compliance Terms Defined
- Compliance automation: Software that automates parts of compliance work, usually evidence collection, control monitoring, and audit preparation. It does not put safeguards in place or train staff for you.
- Continuous monitoring: Automatic, ongoing checks of connected systems against defined controls.
- Evidence collection: Gathering the documents that show compliance. HIPAA documentation is kept for six years under 45 CFR 164.530(j).
- Security Risk Analysis: The documented assessment of risks to electronic protected health information (ePHI) required under 45 CFR 164.308(a)(1)(ii)(A).
- Business Associate Agreement (BAA): A written contract required under 45 CFR 164.502(e) between a covered entity and any vendor that creates, receives, maintains, or transmits protected health information (PHI).
FAQ
Is Sprinto a good choice for HIPAA compliance?
Sprinto supports HIPAA as one of the 25+ frameworks its pricing page says it automates, alongside SOC 2 and ISO 27001. If HIPAA is your only or main need, a HIPAA-specific solution will be faster, simpler, and a better fit for how healthcare compliance works.
Does Sprinto replace the need for a risk assessment?
No. Sprinto's pricing page lists periodic risk assessments, which give you a place to run one. HIPAA still needs a documented risk analysis of your own ePHI. That analysis must identify threats, gaps, and the chance and impact of a breach. A proper risk assessment goes well beyond what automated monitoring covers.
How quickly can a small practice become HIPAA compliant?
With the right approach, a small practice can finish the core work in weeks, not months. That includes the risk assessment, policies, BAAs, and staff training. The timeline depends on how the work is set up and whether you use automation or manual steps.
What do the new HIPAA Security Rule changes in 2026 mean for compliance tools?
The proposed Security Rule updates would add new technical rules. These include MFA, encryption standards, and tighter incident response timelines. They are proposed, not final, so the current Security Rule still applies. Make sure your solution covers the current rule and can adapt if the proposal becomes final. Learn more about the new HIPAA Security Rule changes in 2026.
Can I use Sprinto for SOC 2 and One Guy Consulting for HIPAA?
Yes. Sprinto can handle SOC 2 and ISO 27001 while a HIPAA-specific solution handles healthcare compliance. The two solve different problems and can work side by side.
Key stat: Automated audit platforms reduce the time spent collecting compliance evidence, but the 2026 HIPAA Security Rule changes propose eliminating the distinction between required and addressable implementation specifications. If finalized, every safeguard becomes mandatory - making expert interpretation of the requirements more important than automated tracking of them.
Sources
- 45 CFR Part 164 - Security and Privacy Rules
- HHS OCR Enforcement Actions
- Sprinto Pricing & Plans (checked November 7, 2026)
- Sprinto HIPAA framework page (checked November 7, 2026)
Related Reading
- Compliancy Group vs One Guy Consulting (2026)
- Accountable vs One Guy Consulting (2026)
- Paubox vs One Guy Consulting (2026)
- Drata vs One Guy Consulting (2026)
- Secureframe vs One Guy Consulting (2026)
- Vanta vs One Guy Consulting (2026)
- Dot Compliance vs One Guy Consulting (2026)
Related: What Is HIPAA Certification? Why It Does Not Exist
For a small practice weighing the two, here is what One Guy Consulting's HIPAA compliance software includes.
Try three One Guy Consulting 3D staff training courses free →
Frequently Asked Questions
Is Sprinto designed for HIPAA compliance?
Sprinto lists 25+ frameworks automated out of the box, and HIPAA is one of them, with its own HIPAA page and a Sprinto For Healthcare page. Sprinto describes its Foundation plan as for startups on their first certification and its Growth plan as for teams automating compliance.
What does Sprinto cover for HIPAA?
Sprinto's pricing page lists continuous monitoring across 300+ integrations, automated evidence collection, AI-assisted policies, ready-to-use training and tests, periodic vendor reviews, periodic risk assessments, a risk library, risk treatment plan record and tracking, and a public trust center. Its HIPAA page says its compliance team helps align administrative, physical, and technical safeguards for PHI.
What is the difference between Sprinto and One Guy Consulting for HIPAA?
Sprinto is a compliance automation platform that covers many frameworks and connects to systems such as AWS, Okta, and Google Workspace to collect evidence. One Guy Consulting covers HIPAA only: software that walks a covered entity or business associate through its risk analysis, policies, training, and BAAs, with 1:1 implementation calls on the Full-Scope plan.