HIPAA Gap Analysis: Compliancy Group vs One Guy Consulting
Choose Compliancy Group if you want dedicated Compliance Coach support while your team builds its own remediation plan (your to-do list for fixing the gaps). Choose One Guy Consulting if you want the portal to build the gap analysis and remediation plan from your Security Risk Assessment the moment you submit it.
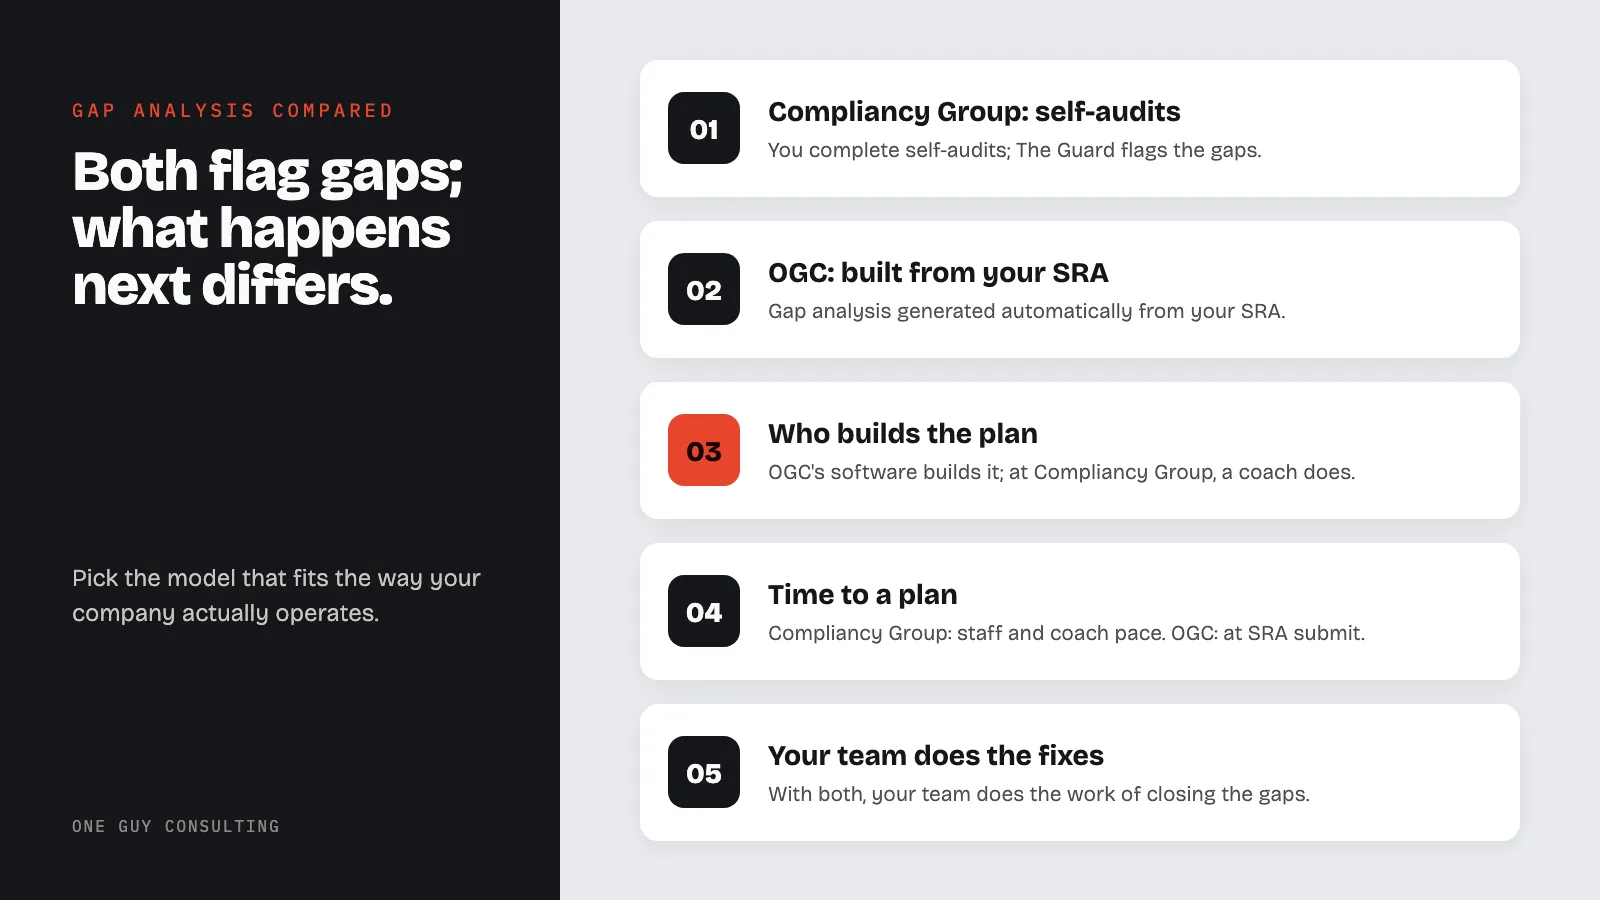
This article breaks down how each company handles HIPAA gap analysis so you can decide which model fits the way your company actually operates.
Key Takeaways
- Compliancy Group runs gap analysis in its platform, The Guard. You complete self-audits, and The Guard flags the gaps. Then you create a remediation plan from the self-audit findings, with dedicated Compliance Coach support.
- One Guy Consulting generates the gap analysis automatically from your Security Risk Assessment, then auto-builds a remediation plan.
- With Compliancy Group, timing depends on two things: how fast your staff finish the self-audits, and how soon your team builds the plans. With One Guy Consulting, the gap analysis and remediation plan are ready the moment you submit the SRA.
- Choose Compliancy Group if you want dedicated Compliance Coach support. Choose One Guy Consulting if you need gaps found fast and want the software to handle the busywork while your team closes them.
Key Terms Defined
- Security Risk Assessment (SRA): A careful check of
the risks to your electronic PHI (patient health information you store or
send electronically). It looks at what could expose that information,
change it, or keep you from getting to it. The rule calls this an
accurate and thorough assessment
, and it is required by 45 CFR 164.308(a)(1)(ii)(A). OCR is the HHS Office for Civil Rights, the agency that enforces HIPAA. In late 2024 it launched a Risk Analysis Initiative aimed at this exact requirement. - Gap analysis: The comparison of your current safeguards against HIPAA’s requirements to find where you fall short. It follows the SRA and feeds the remediation plan.
- Remediation: The work of closing each identified gap. A remediation plan lists those actions with an owner, a due date, and evidence requirements for every item.
- Safeguards: The administrative (45 CFR 164.308), physical (45 CFR 164.310), and technical (45 CFR 164.312) protections HIPAA requires for electronic PHI.
- The Guard: Compliancy Group’s compliance-management platform, where you complete self-audits and the software flags your gaps.
Compliancy Group Gap Analysis vs One Guy Consulting: How Each Approach Works
Both companies use software to flag gaps. The difference is what happens next. At Compliancy Group, you create a remediation plan from the findings of your self-audit, with dedicated Compliance Coach support. At One Guy Consulting, the portal builds the remediation plan for you. It uses the same Security Risk Assessment that found the gaps. With both, your team does the work of closing the gaps.
Quick Comparison: Full Platform Overview
| Category | Compliancy Group | One Guy Consulting |
|---|---|---|
| Method | Self-audits in The Guard, guided by Compliance Coaches | Automated pipeline from SRA to gap analysis to remediation |
| Support Model | Dedicated Compliance Coach support | 4 hours a month of 1:1 implementation calls with Chuck (Full-Scope plan) |
| Gap Analysis Approach | Self-audits, mostly yes or no questions; The Guard flags the gaps | Auto-generated from Security Risk Assessment responses |
| Policy Delivery | Custom policies and procedures created with help from a Compliance Coach | Policy and procedure templates delivered through the compliance portal |
| Training Delivery | Built-in training modules with tracking | Staff training with progress tracking and automated annual reminders |
| BAA Management | Vendor questionnaires sent through The Guard; vendor gaps get remediation plans | Vendors sign their BAAs online, and the portal stores and tracks the signed agreements |
| Typical Timeline | Depends on how fast your staff finish the self-audits and how soon your team builds the plans | Gap analysis and remediation plan ready the moment you submit the SRA |
| Pricing Model | Quote on request; last public list (archived July 28, 2026) started at $99 to $449 a month billed annually, plus $8 to $10 per employee per month | Full-Scope: $120 a month, $1,300 for 12 months, or $2,300 for 24 months (flat rate per location) |
Quick Comparison: Gap Analysis Approach
| Feature | Compliancy Group | One Guy Consulting |
|---|---|---|
| Gap Analysis Method | Self-audits in The Guard; gaps flagged automatically | Automated from Security Risk Assessment results |
| Evidence Collection | You upload and organize it in The Guard | Each plan item lists the proof you need to show it is done |
| Remediation Planning | You create it from your self-audit findings, with dedicated Compliance Coach support | Auto-generated from the gap analysis |
| Time to Actionable Results | Depends on how fast your staff finish the self-audits and build the plans | The moment you submit the SRA |
| Platform Management Required | Yes: your staff complete the self-audits in The Guard | Minimal: the portal builds the gap analysis and plan |
| Best For | Practices that want dedicated Compliance Coach support | Practices that want gaps found fast, with the busywork automated |
How Compliancy Group Handles Gap Analysis
Compliancy Group uses The Guard, their compliance management platform, to walk companies through HIPAA requirements. The process works like this:
- You log into The Guard and complete its self-audits. Most are yes or no questions.
- The Guard flags gaps automatically from your answers.
- You create a remediation plan based on the findings of the self-audit.
- Evidence is uploaded and organized within the platform.
- A compliance coach provides guidance along the way.
This model has strengths. The coaching support is real, and companies that have the time and staff to work through the platform methodically can get solid results.
The real question: how much of the work do you want the software to do, and how much do you want a coach to do?
Where The Guard Leaves Work With You
Three things to know about this model.
You Still Answer Every Self-Audit. The Guard flags gaps, but only from your answers. You go through each self-audit and answer each question.
If you answer a question wrong, the gap may not show up. That is true of any questionnaire, including an SRA.
Evidence Collection Is on You. Once the gaps are found, you gather proof that each fix is done. Then you upload and organize that proof in The Guard. The platform does not pull evidence from your systems. You bring it to the platform.
Your Team Builds the Remediation Plan. Compliancy Group's own page lists the step as Create a remediation plan based on the findings of the self audit
(checked October 30, 2026). So your team builds the plan from its self-audit findings, with dedicated Compliance Coach support, and then carries it out.
How One Guy Consulting Automates Gap Analysis
OGC's gap analysis works differently. You answer the risk assessment questions in the portal, and the system generates the gap analysis from your Security Risk Assessment results.
Here's the pipeline:
- Complete the SRA inside the portal: a guided questionnaire covering administrative safeguards (45 CFR 164.308), physical safeguards (45 CFR 164.310), and technical safeguards (45 CFR 164.312).
- Gap analysis generates automatically: it is ready the moment you submit the SRA. No separate engagement, no second platform, no report to write by hand.
- Remediation plans auto-generate: the portal builds them from the gaps the analysis finds.
- Track progress in one place: a compliance dashboard shows your progress.
No separate gap analysis engagement. No building remediation plans from scratch. The SRA feeds the gap analysis, and the gap analysis feeds the remediation plan. One pipeline.
What the Automation Replaces
Here's what the portal does for you:
- Manual gap identification becomes automatic comparison of SRA responses against HIPAA requirements.
- Manual remediation planning becomes auto-generated remediation plans.
- Manual evidence tracking becomes a plan where each item lists the proof you need to show it is done.
- Manual progress reporting becomes a compliance dashboard. Training tracking and vendor management live in the same portal.
The key difference: at OGC, the software builds the remediation plan. At Compliancy Group, your team builds it from the self-audit findings. Either way, your team still makes the fixes.
Different Philosophies, Same Regulation
Compliancy Group's model:
- Your team completes the self-audits in The Guard.
- The Guard flags gaps automatically from your answers.
- Your team creates the remediation plan from the self-audit findings.
- Coaches guide you through the whole process of putting the plans in place.
One Guy Consulting believes:
- Many small practices don't have compliance staff to train.
- Time spent navigating a platform is time not spent on patient care.
- Software should do the busywork so your team can focus on the fixes.
- A finished remediation plan matters more than the process of building one.
Both approaches can work. The question is which one matches your organization's reality.
Why Gap Analysis Speed Matters in 2026
If you are shopping for a gap analysis tool, you may already be behind on compliance. In late 2024, OCR launched a Risk Analysis Initiative aimed at the SRA. Written policies need to be implemented and tailored to your practice, not just downloaded from a template library. Staff training must be documented. 45 CFR 164.530(b)(2)(ii) says you must keep a record that the training was given.
A practice that's already behind needs two things: its gaps found, and a remediation plan it can start on right away.
In Case 01 of our anonymized case studies, a Florida mental health franchise office had policies never written, records with holes, training half done, and a state auditor due in days. It was audit-ready in under a week and passed its state audit.
With HIPAA fines increasing in 2026, every gap you leave open is a risk you carry until you close it.
What Each Platform Actually Delivers
Compliancy Group (The Guard) delivers:
- Built-in self-audits, most with yes or no questions.
- Dedicated Compliance Coach support.
- Custom policies and procedures created with help from a Compliance Coach.
- Training modules with built-in tracking.
- A HIPAA Seal of Compliance after completing their program (this is a vendor-issued badge, not a government certification).
- Automatic gap flagging from your self-audit answers.
- Remediation plans you create from your self-audit findings.
One Guy Consulting delivers:
- An automated pipeline where the SRA feeds directly into gap detection and remediation planning.
- 4 hours a month of 1:1 implementation calls with Chuck (Full-Scope plan).
- Policy and procedure templates delivered through the compliance portal.
- Automated BAA execution where vendors sign online and agreements are stored and tracked.
- Remediation plans auto-generated from the gap analysis.
- A compliance dashboard that tracks your progress.
Best Fit
Choose Compliancy Group if:
- You have a dedicated compliance officer with bandwidth to work through The Guard.
- You want to build internal compliance management capability over time.
- Your company is mostly compliant and needs a structured way to maintain it.
- You prefer guided coaching over automated output.
- You want dedicated Compliance Coach support.
Choose One Guy Consulting if:
- You need gaps identified and remediation started right away.
- You don't have staff to dedicate to platform navigation.
- Your company is behind on compliance and needs to catch up fast.
- You want the SRA, gap analysis, and remediation plan connected in one automated pipeline.
- You want 1:1 implementation calls with the person who built the process (Full-Scope plan).
Final Take
Compliancy Group pairs its software with dedicated Compliance Coach support, and your team builds the remediation plan from its self-audit findings. One Guy Consulting's portal builds the gap analysis and remediation plan for you the moment you submit your SRA. Your team still does the work, and on the Full-Scope plan Chuck walks you through it. For practices already behind on Security Risk Assessments, BAA management, and policy records, that difference decides how fast you get a plan in hand.
One Guy Consulting in 37 seconds
Related Reading
- Compliancy Group vs One Guy Consulting: Which HIPAA Solution to Pick?: The full platform comparison.
- Accountable vs One Guy Consulting: HIPAA Compliance Compared: Another competitor breakdown.
- How to Conduct a HIPAA Risk Assessment: The SRA that feeds your gap analysis.
- HIPAA Fines Increased in 2026: Updated Penalty Amounts: Why gap closure speed matters.
FAQ
What is the main difference between Compliancy Group and One Guy Consulting for HIPAA gap analysis?
With Compliancy Group, you complete self-audits in The Guard and the software flags your gaps. Then you create a remediation plan from those findings, with dedicated Compliance Coach support. With One Guy Consulting, your Security Risk Assessment feeds straight into an automatic gap analysis. The portal then builds your remediation plan from it.
Which is faster for finding HIPAA compliance gaps?
One Guy Consulting's gap analysis and remediation plan are ready the moment you submit your Security Risk Assessment. With Compliancy Group, The Guard flags gaps once your self-audits are done. Your team then builds the remediation plan from those findings. So timing depends on how fast your staff finish the self-audits and build the plans.
Does Compliancy Group automate their gap analysis?
Yes, for finding gaps. Compliancy Group's Why The Guard page lists "A Simple Self Auditing Solution" with "Gap Identification & Remediation" (checked October 30, 2026). Your team then creates the remediation plan from the self-audit findings. At One Guy Consulting, the software builds both the gap analysis and the remediation plan.
Do I need a separate gap analysis engagement with One Guy Consulting?
No. The gap analysis generates automatically from your Security Risk Assessment results inside the OGC portal. There is no separate engagement, no extra cost, and no manual report assembly required.
Which is better if my company is already behind on HIPAA compliance?
One Guy Consulting is built for companies that are behind. The portal finds your gaps and builds a remediation plan the moment you submit your SRA, so you can start the same day. Compliancy Group's model needs two steps first: your staff finish the self-audits, then build the plans. That extra step matters when you are under time pressure from enforcement risk or upcoming audits.
Try three One Guy Consulting 3D staff training courses free →