By Chuck Weiselberg, Founder, One Guy Consulting. Published .
Chuck Weiselberg, Founder, One Guy Consulting; Certified HIPAA Professional (CHP); 10 years of HIPAA compliance experience. Full author bio
A Business Associate Agreement (BAA) is a HIPAA-required contract for vendors that handle PHI. A confidentiality agreement alone does not satisfy HIPAA.
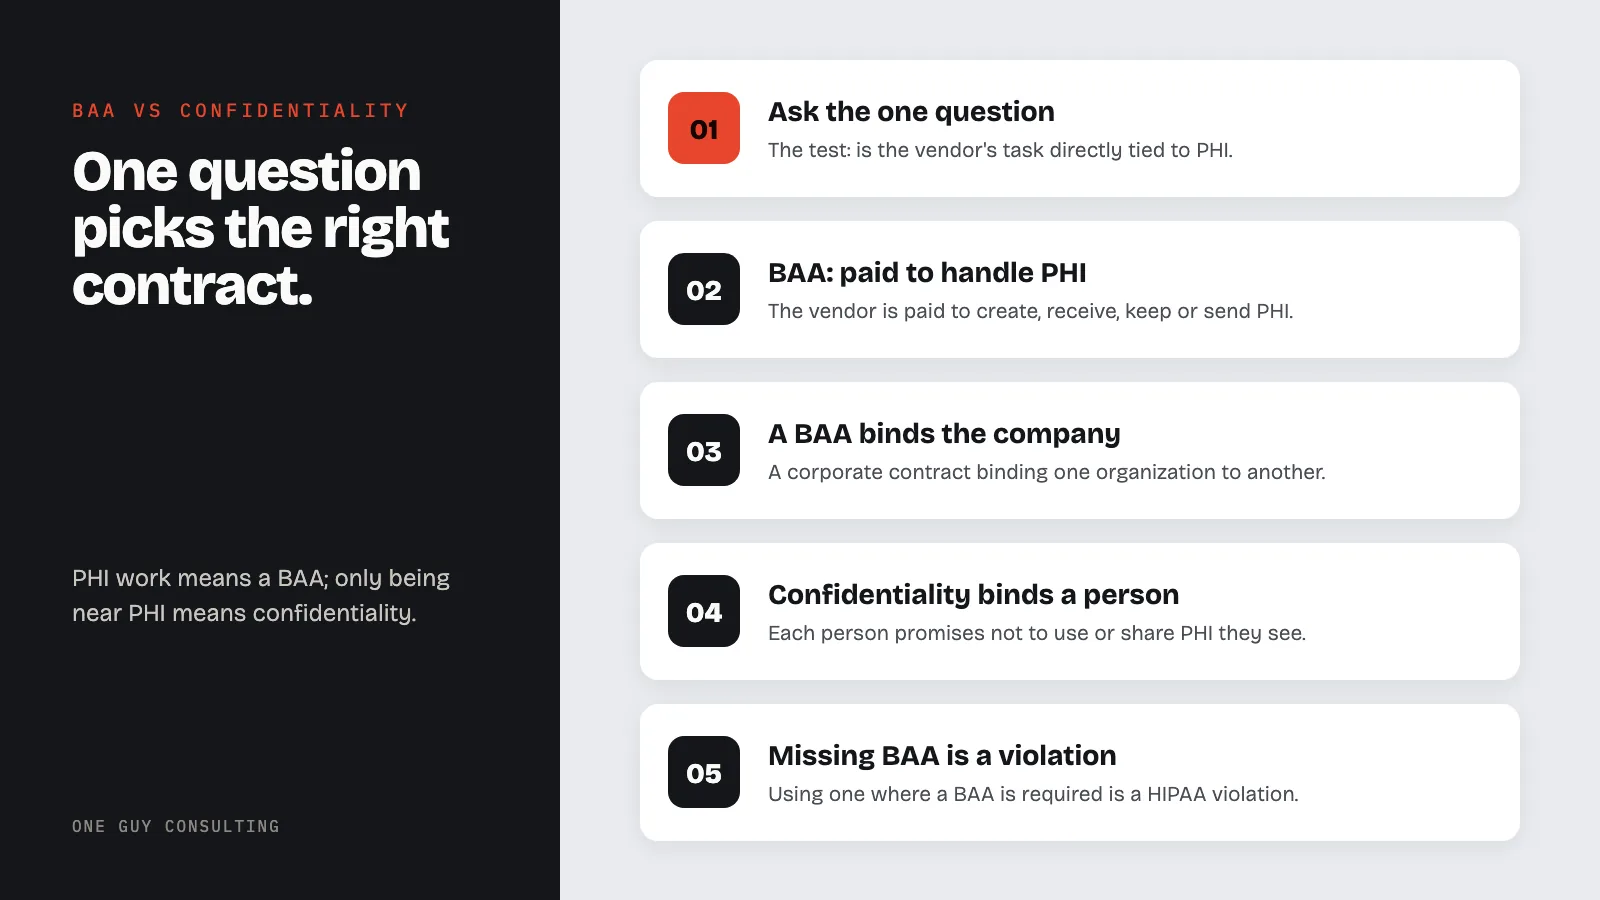
Vendors whose job is directly tied to PHI (protected health information: individually identifiable health data) sign a BAA (Business Associate Agreement: a written contract governing vendors that handle PHI); vendors who are only in your office near PHI sign a confidentiality agreement (a contract to keep information private, but not HIPAA-specific). A vendor paid to create, receive, keep, or send PHI is a business associate under 45 CFR 160.103. The water delivery person, mail carrier, and HVAC tech are not.
In June 2023, OCR settled with iHealth Solutions for $75,000. iHealth was a business associate, which means a vendor that handles patient health information for a practice. The ePHI (electronic patient health information) of 267 individuals was taken from an unsecured server. OCR also found the company had not done a risk analysis [1]. Vendors who handle PHI have real HIPAA duties. The business associate agreements you sign with them put those duties in writing. The wrong contract (or no contract at all) is also one of the easiest HIPAA problems to prevent.
But here is the part that trips up every practice manager: not every person who walks through your door needs a business associate agreement (BAA). Some of them need a confidentiality agreement instead. Knowing which contract applies to which vendor is not a gray area. There is one question that answers it every time.
When to use a BAA vs a confidentiality agreement
The distinction between a BAA and a confidentiality agreement is not about the size of the company, the frequency of their visits, or how much PHI they might see. It is about one thing: the task they are being paid to perform.
When Is a BAA Required? Is Their Task Directly Tied to PHI?
That is the only question. If the answer is yes, meaning the vendor is being expressly paid to create, receive, maintain, or transmit protected health information (PHI) as part of their job, they are a business associate under 45 CFR 160.103, and a BAA is required before they touch a single record.
If the answer is no, meaning the vendor’s task has nothing to do with PHI, but they happen to be inside your office where PHI exists, they are not a business associate. They do not need a BAA. But you still have a compliance risk to manage. That is where a confidentiality agreement comes in.
This is the line that most compliance content ignores entirely. They tell you “sign a BAA with your vendors” and leave it at that. But you have vendors, contractors, and service people coming in and out of your office space every single day. Not all of them are business associates. Treating them all the same creates unnecessary overhead, confuses your vendor management, and can actually weaken your compliance posture by diluting what a BAA is supposed to mean.
What is a Business Associate Agreement (BAA)?
A BAA is a corporate-level contract that works from the top down. It binds one organization to another. It imposes obligations under the HIPAA Privacy Rule and Security Rule. It requires the business associate to implement administrative, physical, and technical safeguards. It mandates breach notification. It gives you the right to terminate the relationship if they violate the agreement [2].
A BAA is required under 45 CFR 164.504(e) whenever a covered entity engages a vendor whose function, activity, or service involves the use or disclosure of PHI.
The relationship is built around PHI. The vendor exists in your workflow specifically because you need them to handle patient data. Examples:
- Your EHR vendor stores and transmits patient records
- Your billing company processes claims containing diagnosis codes and patient identifiers
- Your IT managed service provider has access to systems containing ePHI
- Your cloud backup provider stores encrypted copies of your patient database
- Your shredding company destroys documents containing PHI
- A consultant you hire to conduct a risk assessment reviews your PHI workflows
Every one of these vendors is being paid to do a job that is directly related to protected health information. The BAA is the contract that makes that relationship HIPAA-compliant.
What is a confidentiality agreement?
A confidentiality agreement is the opposite of a BAA in almost every structural way. Where a BAA is corporate (binding one organization to another from the top down), a confidentiality agreement is personal. It is a person-to-person contract. The individual signing it is declaring: I am here to do my job. If I happen to see protected health information while I am on these premises, I will not use it, share it, or disclose it to anyone.
That is it. No Security Rule obligations. No breach notification procedures. No audit rights. No subcontractor flow-down requirements. It is a focused, narrow agreement that addresses a specific, limited risk: someone who is not there to work with PHI might accidentally encounter it.
A confidentiality agreement does not make someone a business associate. It does not impose HIPAA obligations on them. What it does is create a documented safeguard: evidence that you identified the risk of incidental PHI exposure, took a reasonable step to mitigate it, and put it in writing. That is the kind of record that helps if OCR ever investigates your practice.
The Water Guy, the Mail Carrier, and the Sharps Collector
Think about the people who walk through your office on any given week. The person who delivers your water. The mail carrier. Someone from a medical waste company who picks up your sharps containers. The HVAC technician. A copier repair tech.
None of these people are being paid to work with PHI. The water delivery person is there to swap out a jug. The sharps collector is there to pick up a biohazard container. Their task has zero to do with patient data.
But they are inside your four walls. They walk past the front desk. They might see a patient sign-in sheet. They could glance at a screen showing a patient schedule. They might overhear a phone call. The sharps collector walks through clinical areas where charts, labels, and documents with PHI are visible.
HHS OCR (the HHS Office for Civil Rights, which enforces HIPAA) has addressed this directly. In FAQ 243, HHS states that a business associate contract is not required with persons whose functions:
"do not involve the use or disclosure of protected health information, and where any access to protected health information by such persons would be incidental, if at all"
(HHS OCR, FAQ 243) [3]
Incidental means it was not the purpose of their visit. It was not part of their job. It was a by-product of being physically present in a space where PHI exists.
But “no BAA required” does not mean “no action required.” You still have an obligation under the Privacy Rule to implement reasonable safeguards to limit incidental disclosures (45 CFR 164.530(c)). A confidentiality agreement is one of those safeguards. It puts the individual on notice that they may encounter sensitive information, and it documents their commitment to keep it private.
Key legal differences under HIPAA
| Business Associate Agreement | Confidentiality Agreement | |
|---|---|---|
| Type of contract | Corporate, organization-to-organization | Personal, individual-to-organization |
| Direction | Top-down (binds the company) | Bottom-up (binds the person) |
| When required | Vendor’s task is directly tied to PHI | Vendor may incidentally encounter PHI |
| HIPAA mandate | Required under 45 CFR 164.504(e) | Not HIPAA-mandated, but a reasonable safeguard |
| Scope | Privacy Rule, Security Rule, breach notification, subcontractor obligations | Promise not to use or disclose PHI |
| Examples | EHR vendor, billing company, IT provider, shredding company | Water delivery, mail carrier, sharps collector, HVAC tech |
| Termination rights | Yes, for material breach | Typically not applicable |
| Breach notification | Required within 60 days of discovery | Not required |
Checklist: what to include in a BAA
These are the required BAA clauses. Under 45 CFR 164.504(e)(2), a contract between a covered entity (a health plan, clearinghouse, or provider that bills electronically) and a business associate must:
- Establish the permitted and required uses and disclosures of PHI by the business associate.
- Bar any use or further disclosure other than as the contract permits or the law requires.
- Require appropriate safeguards, and Security Rule compliance for electronic PHI.
- Require reports of any use or disclosure not provided for by the contract, including breaches of unsecured PHI under 164.410 (no later than 60 days after discovery).
- Require subcontractors that handle PHI to agree to the same restrictions.
- Make PHI available for patient access, amendment, and an accounting of disclosures (164.524, 164.526, 164.528).
- Carry out any Privacy Rule obligation the business associate performs for the covered entity in compliance with that rule.
- Make its books and records available to HHS for compliance review.
- Return or destroy PHI at termination, if feasible.
- Authorize termination by the covered entity if the business associate violates a material term.
The HHS model BAA provisions follow this list.
Who signs a BAA?
A BAA is signed by the two organizations, through someone authorized to bind each one: the covered entity (the practice) and the business associate (the vendor company). A business associate that hands PHI work to its own subcontractor signs a BAA with that subcontractor too (164.502(e)(1)(ii)). A confidentiality agreement, by contrast, is signed by the individual who comes into the office.
What Happens When You Pick the Wrong One
Getting it wrong in either direction creates problems.
Signing a BAA when a confidentiality agreement would suffice creates administrative bloat. You are now tracking that vendor as a business associate. You must tell them about any limits in your Notice of Privacy Practices. You need to monitor their compliance. You may need to verify their safeguards annually. For the water delivery company, that is absurd, and it dilutes your attention from the vendors who actually handle PHI and present real risk.
Signing a confidentiality agreement when a BAA is required is a HIPAA violation. If a vendor is creating, receiving, maintaining, or transmitting PHI on your behalf and you do not have a BAA in place, you are in violation of 45 CFR 164.502(e) regardless of whether a breach ever happens. OCR does not need a breach to find a violation: the missing contract alone is enough.
Penalties for missing BAAs range from $145 to $73,011 per violation. The top tier is willful neglect, which means ignoring the rules on purpose or with reckless disregard. If that is not corrected, one violation can cost up to $2,190,294. Each violation category also has a yearly cap of up to $2,190,294 [4].
The test is always the same: is the vendor’s task directly tied to PHI? If you have to think about it for more than a few seconds, the answer is usually clear once you ask the question the right way.
Case note (anonymized, from One Guy Consulting's case studies): during a wider program review, a practice found several vendors touching PHI with no BAA in place. It got every missing BAA signed and set up a vendor review it can run again. Read case 05.
Glossary
- PHI: individually identifiable health information held or sent by a covered entity or business associate (160.103).
- Covered entity: a health plan, health care clearinghouse, or health care provider that sends health information electronically for standard transactions.
- Business associate: a person or company that creates, receives, maintains, or transmits PHI on a covered entity's behalf.
- Breach notification: the duty to tell patients, HHS, and sometimes the media after a breach of unsecured PHI (164.404 to 164.410).
- Minimum necessary: using or sharing only the PHI needed for the task (164.502(b)).
- Encryption: scrambling data so only key holders can read it; addressable under 164.312(a)(2)(iv).
FAQs
Do I need a BAA or a confidentiality agreement?
If a vendor handles PHI, you need a BAA; a confidentiality agreement alone does not meet HIPAA.
What clauses must a BAA include?
A BAA must assign PHI safeguards and breach-notification duties between parties under HIPAA.
Can a confidentiality agreement replace a BAA?
No; confidentiality agreements lack HIPAA-specific PHI handling and reporting requirements.
Sources
- HHS OCR: iHealth Solutions Settlement, June 2023
- HHS: Business Associates Guidance
- HHS FAQ 243: Business Associate Contract for Inadvertent Contact with PHI
- HIPAA Fines Increased in 2026
- 45 CFR 160.103: Definition of Business Associate
- 45 CFR 164.504(e): Business Associate Contract Requirements
- HHS Model Business Associate Agreement
Related Reading
- Business Associate Agreement: Complete Guide
- 7 Business Associate Agreement Mistakes That Lead to HIPAA Fines
- Business Associate Agreements: What They Are and Why You Need One
- HIPAA Risk Assessments for Business Associates
- Change Healthcare Breach: One Year Later
- HIPAA for Marketing Agencies: A Compliance Guide
One Guy Consulting offers affordable HIPAA compliance packages for practices of all sizes. See HIPAA compliance packages
This content is for educational and informational purposes only and should not be construed as legal advice.
Try three One Guy Consulting 3D staff training courses free →